Publicaciones Publications
Publication of the Business Case of Industrial Cybersecurity notebook
Those responsible for industrial cybersecurity must counter threats and plan based on continuous improvement, in line with the continuous technological and other changes that companies face in order to be competitive.
To prepare a project, or rather, to start it, in many occasions it implies substantial changes in the company and / or the need to do a CAPEX. For the latter, internal conformity is needed. And to obtain it, the most widely used means is to submit the project for formal approval through a business case.
There is not normally the figure of an OT cybersecurity manager in industrial organizations, which implies that another role assumes this responsibility, for example, in some organizations the operational security manager or the physical security manager assumes this responsibility, in other organizations it is the person in charge of operations or the person in charge of communications, although it is the person in charge of information security who is usually in charge of industrial cybersecurity. This situation has been taken into account in the development of this document.
This document is available to active subscription members of CCI at the knowledge platform.
The document can be acquired by requesting it from info@cci-es.org
Title
19/10/2026
This study analyzes the maturity level of food sector organizations against high-impact cyber incidents, understood as their actual capability to protect, sustain, and recover their critical industrial processes. The study combines an industry survey on the operational, food safety, financial, reputational, environmental, and regulatory impact of various cyber incidents with an industrial cybersecurity maturity assessment […]
01/10/2026
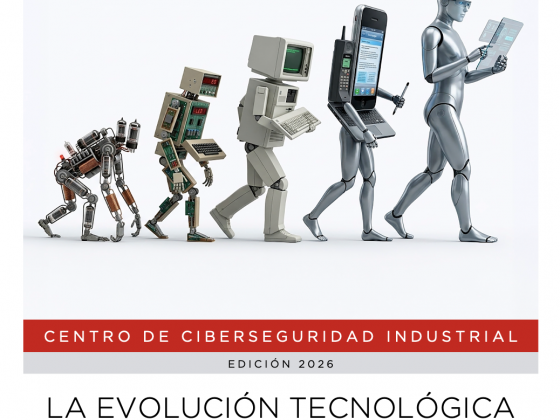
This document analyzes how technological and industrial evolution is not the result of perfect designs, but of a cumulative process of patches, adaptations, and dependencies that generate digital fragility. Through five strategic rules and a common language (D-P-R), it proposes transforming this inevitable imperfection into operational resilience and human sovereignty.

09/09/2026
This guide does not intend to define a single model for a Cybersecurity Operations Center, but rather to provide criteria, capabilities, recommendations, and best practices to build, evolve, or adapt a SOC progressively, aligning it with the operational reality of each industrial organization.
07/07/2026
This guide presents the SG2CI, an industrial cybersecurity governance and management operating system that enables the ICSO to govern, coordinate, and evolve cybersecurity in a complex, interdependent, and changing industrial environment. SG2CI does not intend to replace standards such as IEC 62443, ISO 27001, or the NIST CSF 2.0. SG2CI is an evolution of SGCI, […]